Work / Desktop AI team, open source / 2026
OpenDot
A Mac and Windows app that runs a team of AI assistants on your own computer, with a permission system between every one of them.
The boundary
Stays inside
- Mail, calendar, files and notes
- API keys and OAuth tokens (Keychain or DPAPI)
- Plain JSON state in ~/.opendot
- Audit log, contents left out
Allowed to cross
- Prompts with emails, phones and cards masked
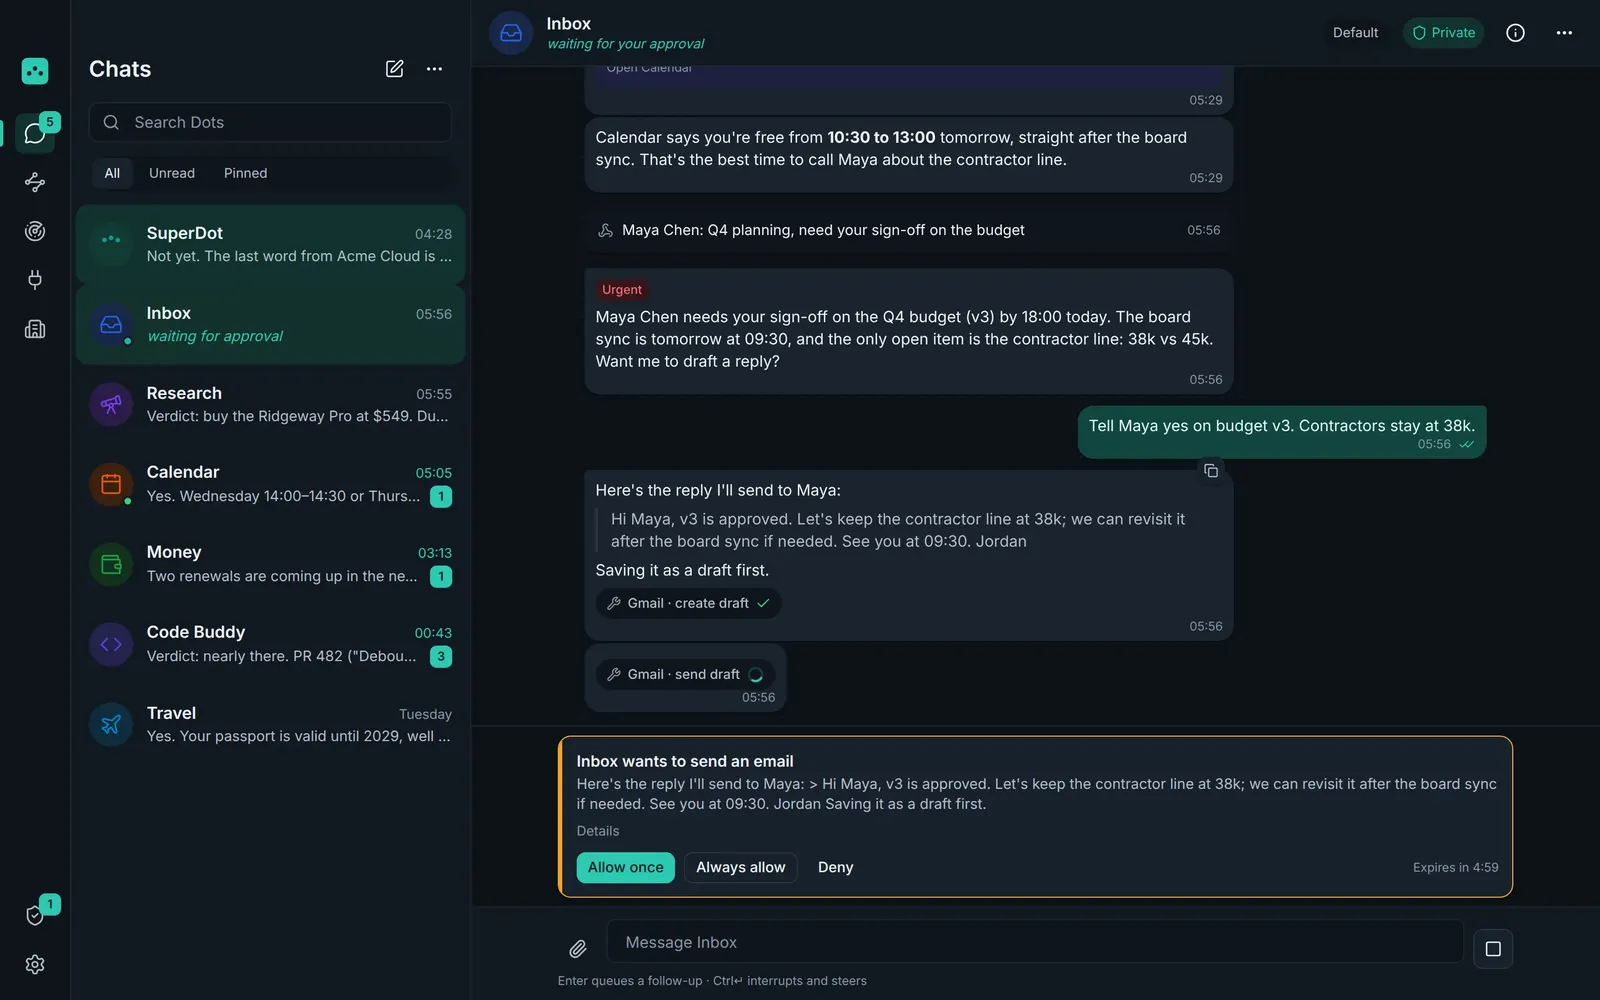
- Tool calls that change the world, after your yes
Nothing that changes the world happens without your yes.
Context
Agent apps ask for your inbox, your files and your shell, then send all of it to a cloud model. One prompt injection in an email is enough to make an assistant act for someone else.
Idea
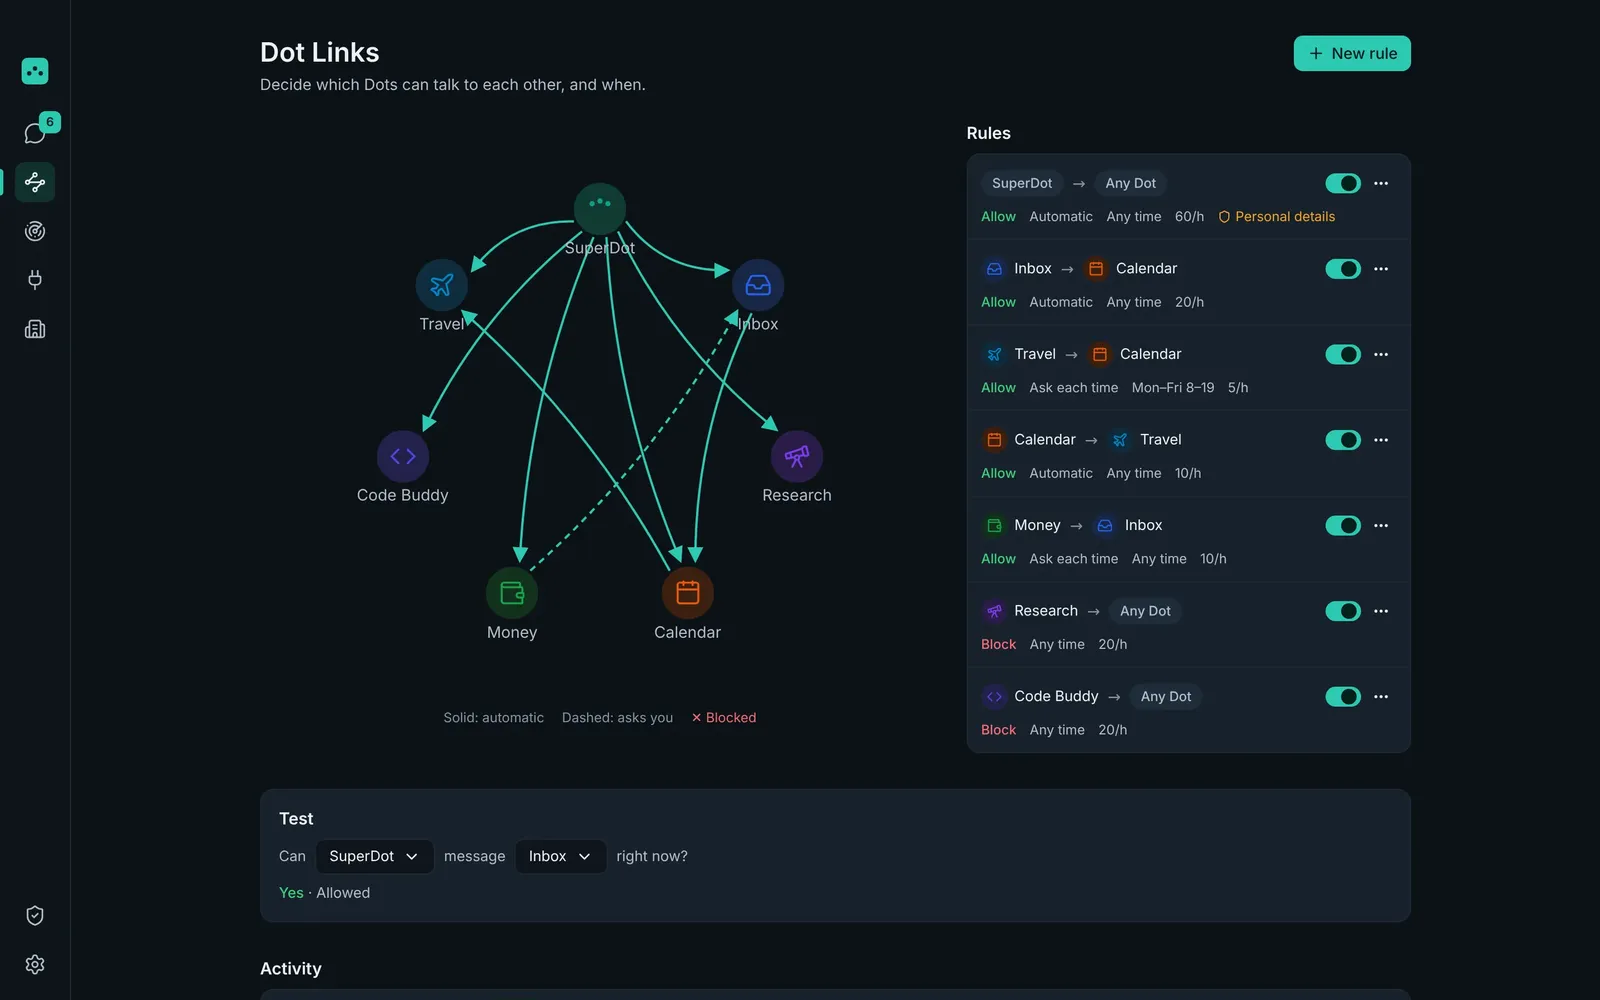
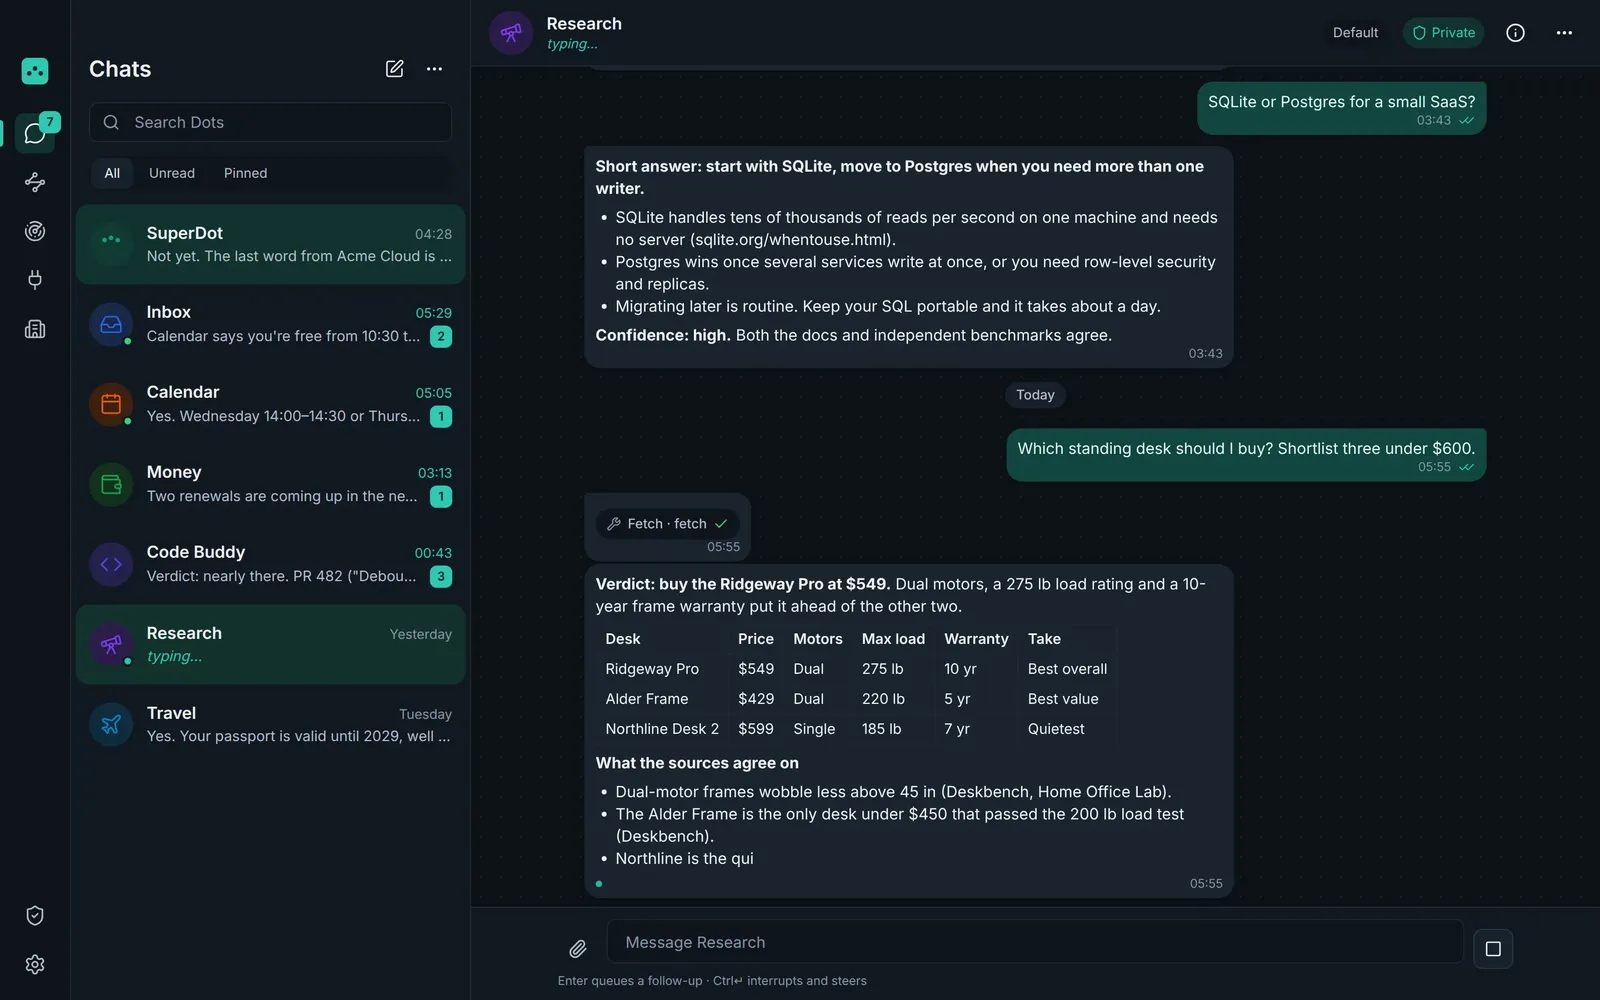
Split the assistant into Dots that each own one job and only the access you grant. Put a policy layer between them, Dot Links, where every route is allow, ask or block, with schedules and rate limits. Mask personal details before anything leaves the machine.
Craft
- Secrets are encrypted by the operating system: macOS Keychain or Windows DPAPI, tied to the account.
- An approvals inbox holds every send, delete or run request on one card; unanswered requests expire after five minutes.
- PII masking runs on typed text and file passages alike, and values are restored only locally.
- Organisations: SuperDot plans a project across up to 13 department Dots, runs independent tasks in parallel and waits for your approval of the plan.
- Model agnostic across 8+ cloud providers and local runtimes (Ollama, LM Studio, vLLM), with unlimited MCP servers.
- GitHub Actions builds, tests (Vitest, Playwright end to end) and packages macOS and Windows releases on every commit.
- A public security policy with private advisories, response targets and a scope that names malicious MCP servers and crafted emails.
Threat model
| Asset | Threat | Control |
|---|---|---|
| Inbox and files | Prompt injection in a received email | Tools that act wait in the approvals inbox |
| API keys | Theft from disk or logs | OS-encrypted secrets.bin, never written to logs |
| Personal data | Leak to a cloud model | Masking before send, restore after |
| Dot to Dot traffic | One Dot pivoting through another | Dot Links: allow, ask or block, rate limited and logged |
Outcome
Shipped as an open-source desktop app with CI on every push, desktop release builds from the pipeline and a public site at opendot.live. Works with Claude, GPT, Gemini and fully local models.